Security teams, stop hunting for threats. The cloud has fundamentally reshaped how we build, deploy, and secure applications. Yet, many organizations are stuck playing catch-up, reacting to breaches and incidents instead of preventing them.
The numbers paint a stark picture:
- 81% of organizations experienced cloud-related security incidents in the past year (Venafi).
- Over 55% of breaches were caused by human error (Thales).
- Misconfigurations, a preventable issue, accounted for 32% of incidents (Venafi).
These aren’t isolated issues—they’re systemic, rooted in a lack of proactive visibility and hygiene across sprawling cloud architectures. Without a clear and consistent view of cloud assets, teams are blind to risks lurking in their environments.
Proactive asset visibility and hygiene are more foundational to effective security than reactive threat hunting. It’s time for security teams to shift focus from symptom-chasing to problem-prevention. Building a secure cloud starts with understanding what you have, where it is, and whether it’s configured safely. Let’s dig into why this matters more than ever.
Flaws in Reactive Threat Hunting
Threat hunting, at its core, is the process of actively searching for malicious activity within an environment. In cloud environments, this typically involves analyzing logs, investigating suspicious behavior, and responding to potential threats as they arise. While this approach has its merits, it’s fundamentally reactive—focused on identifying and mitigating threats after they’ve already occurred.
The Pitfalls of Reactive-Only Security
Relying solely on reactive threat hunting comes with significant flaws:
- Focuses on Symptoms, Not Root Causes: Reactive hunting addresses the immediate threat but often ignores the underlying issues, like misconfigurations or outdated access policies, that allowed the threat to exist in the first place.
- Limited by Incomplete or Fragmented Data: Without centralized asset visibility, threat hunting teams are forced to work with siloed or inconsistent data, making it harder to identify patterns or fully understand the scope of potential risks.
- Inefficient for Complex Multi-Cloud Architectures: As organizations expand across multiple cloud platforms, managing the sheer scale of logs and alerts becomes overwhelming. Threat hunting can devolve into chasing false positives or spending time on low-priority issues.
The Real Culprit: Poor Cloud Asset Hygiene
Consider this example: A security team investigates a runtime security incident where unauthorized access was detected. Upon deeper analysis, they discovered that the root cause was an overlooked misconfiguration—an open security group with unrestricted outbound access. This incident wasn’t about missing the threat; it was about missing the vulnerability that enabled it.
Reactive threat hunting might resolve the symptom, but without addressing asset hygiene, the vulnerability remains, waiting to be exploited again. Proactive asset management flips the script, focusing on eliminating these vulnerabilities before they become incidents.
In today’s cloud environments, relying solely on reactive strategies is no longer enough. Security requires a shift toward prevention, built on a foundation of proactive asset visibility and hygiene.
The Case for Proactive Asset Management
Proactive asset management is the foundation of a modern, resilient cloud security strategy. Rather than reacting to incidents as they arise, this approach focuses on preventing vulnerabilities through consistent visibility, monitoring, and hygiene practices. Here’s what it entails:
What is Proactive Asset Management?
- Centralized Visibility of All Cloud Assets: To manage risk effectively, organizations need a unified view of all their cloud assets across providers. This means having a centralized cloud asset inventory that tracks resources, configurations, and changes in real time. Learn more about building a cloud asset inventory.
- Consistent Monitoring Across Clouds: With 69% of organizations using three or more cloud service providers (Enterprise Strategy Group), managing configurations, access policies, and compliance from a single point of control is critical. Proactive monitoring ensures that security teams can detect issues before they escalate.
- Regular Hygiene Practices: Vulnerabilities like misconfigurations or excessive access privileges are often overlooked until they lead to incidents. Routine checks and hygiene practices—such as regular audits and configuration validations—help eliminate these risks proactively.
The Benefits of Proactive Asset Management
- Prevents Incidents Before They Happen: By addressing vulnerabilities early, security teams can stop incidents like unauthorized access or failed audits before they occur.
- Improves Audit Readiness and Compliance: A centralized, well-maintained inventory simplifies compliance with frameworks like SOC 2, HIPAA, and ISO 27001, making audits faster and more efficient.
- Scales with Cloud Complexity: As organizations expand their use of cloud services, proactive management ensures security practices evolve alongside their architectures, avoiding gaps that lead to incidents.
Empowering Decentralized Teams
In a decentralized world of DevOps and platform engineering, teams often work independently. Proactive asset management provides a shared baseline of visibility and controls, empowering teams to manage risks autonomously while adhering to organizational standards.
The stakes are high:
- 45% of organizations experienced 4+ cloud security incidents last year (Venafi).
- Misconfigurations (32%) and unauthorized access (33%) remain the leading causes of incidents (Venafi).
By embracing proactive asset management, security teams can focus on building resilient infrastructures rather than reacting to constant fire drills.
Steps to Implement Proactive Asset Management
Implementing proactive asset management may seem daunting, but by breaking it into manageable steps, security teams can build a foundation for long-term resilience and scalability.
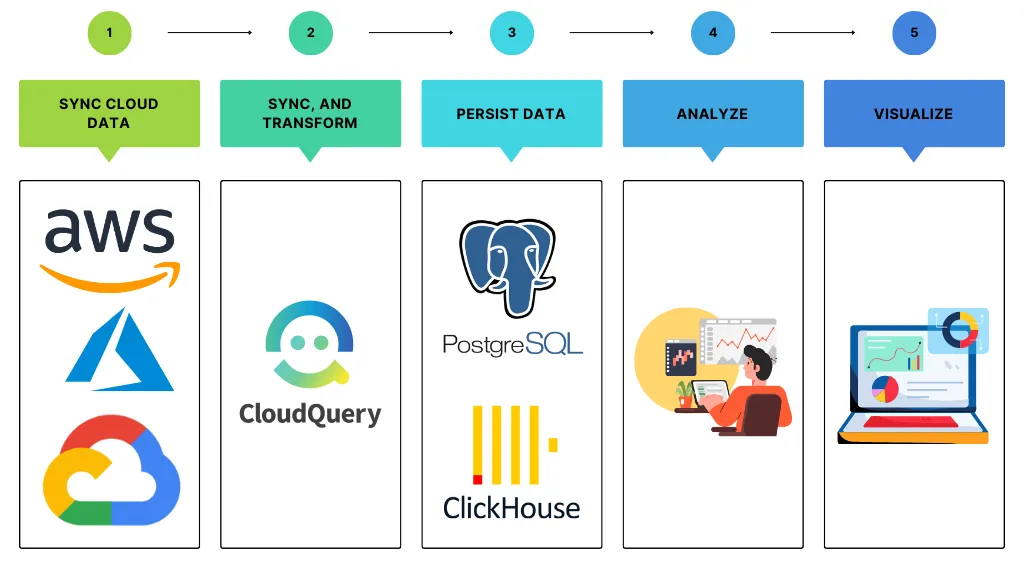
Here’s how to get started:
1. Build a Centralized Asset Inventory
A centralized inventory is the cornerstone of proactive asset management. By unifying data across multi-cloud environments, you gain complete visibility into your cloud assets, including configurations, access policies, and changes. Learn how to build a multi-cloud asset inventory with CloudQuery.
2. Automate Compliance and Monitoring
Manual compliance checks and configuration reviews are time-consuming and prone to error. Instead, automate these processes to ensure continuous monitoring of:
- Compliance with security frameworks (e.g., SOC 2, HIPAA).
- Configurations that adhere to best practices.
- Access controls to minimize unauthorized access risks.
Automation allows security teams to focus on higher-priority tasks while maintaining a secure and compliant cloud environment.
3. Establish Regular Hygiene Practices
Proactive security isn’t a one-and-done activity. Schedule recurring tasks to maintain asset hygiene, such as:
- Conducting periodic vulnerability scans.
- Performing configuration reviews to identify and fix misconfigurations.
- Auditing access policies to remove unnecessary privileges.
These routine practices reduce risk and improve the overall health of your cloud infrastructure.
4. Decentralized Teams Need Centralized Tools
Decentralized teams need tools that provide shared visibility and controls without disrupting their workflows. Equip your teams with platforms like CloudQuery, which enable them to:
- Query and visualize cloud assets with ease.
- Build custom dashboards tailored to their specific needs.
- Collaborate effectively with consistent data and insights.
By providing teams with the right tools, you enable them to take ownership of security while maintaining organizational standards.
Final Thoughts
It’s time to stop fighting fires and start building a resilient cloud infrastructure. Proactive asset visibility isn’t just a strategy—it’s the foundation of modern cloud security. By shifting your focus from reactive threat hunting to proactive management, you empower your teams to prevent incidents, scale effectively, and maintain compliance with confidence.
Proactive security is more than a tool set; it’s a mindset. With the right practices in place—centralized visibility, continuous monitoring, and regular hygiene—you can transform your cloud infrastructure into a secure, scalable, and resilient system.
What’s Next?
Ready to stop chasing threats and start preventing them? Contact us to get started building a centralized asset inventory and implement proactive security today.
Have questions, need support, or want to connect with other CloudQuery developers? Join the CloudQuery Developer Community. It’s the best place to connect with fellow cloud enthusiasts, share insights, get your questions answered, and access a growing library of searchable knowledge.
What’s your team doing to proactively manage cloud security? Join the conversation and share your insights with us on LinkedIn, X, or on our Community Forum.
Written by
Try CloudQuery yourself
Self-hosted, open source, and free to start. Or schedule a demo to see the managed version.