Introducing CloudQuery Alerts
Today, we're shipping Alerts for CloudQuery Platform. This bridges the gap between finding problems and fixing them, letting cloud and platform teams turn visibility into action.
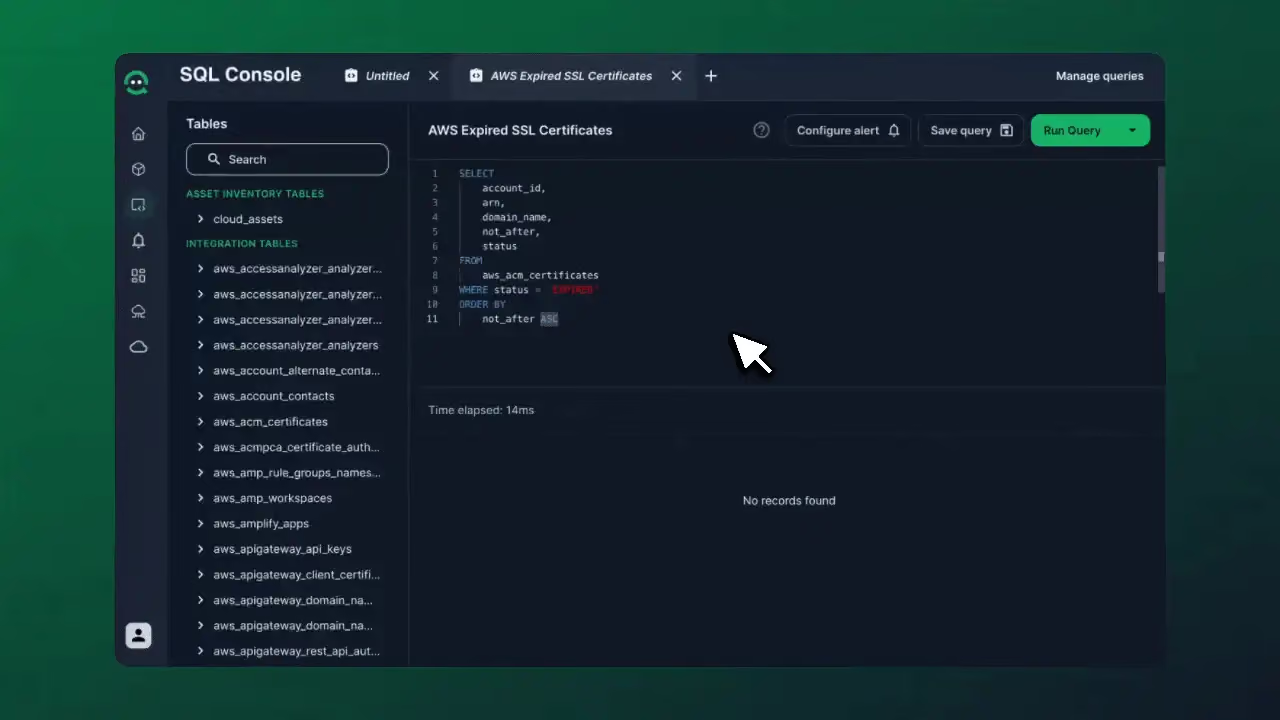
We built alerts because infrastructure teams shouldn't have to babysit dashboards or remember to run queries. Your infrastructure should tell you when something's wrong, not the other way around. After taking feedback from our users and testing with teams managing everything from 50 to 50,000 resources, we've learned what makes alerts actually useful: they need to be dead simple to configure, smart about state management, and flexible enough to integrate with whatever tools you're already using.

CloudQuery alerts work with any SQL query you can write. If you can query it, you can alert on it. That means compliance violations, cost anomalies, security gaps, configuration drift - anything that shows up in your CloudQuery data can now trigger immediate notifications to your team.
Actually Do Something When Your Cloud Config Breaks
The mechanics of an alert in CloudQuery are straightforward: write a SQL query, configure alert destinations, and we handle the rest. When your alert query finds violations, you get notified. When violations clear, you get notified again. No manual checking, no missed incidents.
Configure this as an alert, and you'll know within minutes when someone spins up untagged infrastructure.
What Teams Are Actually Monitoring
Compliance Violations
One financial services team monitors 15,000+ resources across six AWS accounts. Their primary alert catches unencrypted storage:
They get Slack notifications for new violations and Jira tickets for recurring issues.

Cost Anomalies
A startup tracks unattached resources that burn budget:
This saved them $2,400/month in the first quarter. The alert fires to their #infrastructure Slack channel, triggering automated cleanup scripts.
Security Gaps
An e-commerce platform monitors IAM privileges:
They catch overprivileged users before they hit production. Alert frequency dropped 90% after implementing this because teams started following the principle of least privilege.
Webhook Flexibility
Since we use webhooks for notifications, integration possibilities are endless. Teams send alerts to:
- Slack channels with formatted messages
- Jira for automatic ticket creation
- Custom dashboards via HTTP endpoints
- PagerDuty for escalation workflows
- Internal APIs that trigger remediation scripts
The payload structure supports complex integrations. One team built a webhook receiver that automatically creates GitHub issues with query results formatted as markdown tables.
Getting Started
- Write Your Query
Navigate to SQL Console. Write a query that returns rows when something needs attention. Test it against your current data.
- Configure Destinations
Set up notification destinations in Organization Settings. We support webhooks, so you can integrate with Slack, Discord, PagerDuty, or custom endpoints. Configure the payload using our placeholders:
{{query_name}}- alert identifier{{query_url}}- direct link to results{{alert_violations}}- row count returned{{alert_status}}- triggered or inactive
- Enable the Alert
Click "Configure Alert" in SQL Console. Choose severity, set your message, and select destinations. We evaluate alerts after every sync automatically.
Try It Now
Alerts are available immediately for all CloudQuery Platform users. No additional setup required beyond configuring your first notification destination.

Start with a simple query that matters to your team. Add one alert. See how it changes your workflow when infrastructure issues surface automatically instead of hiding in dashboards you never check.
Alerts are powered by SQL and your full, normalized cloud asset inventory, meaning that you aren’t locked into predefined rules or shallow checks. With CloudQuery, you can build exactly what your team needs on top of comprehensive infrastructure data.
Explore CloudQuery's alert documentation to understand implementation patterns, or connect with the community to see how other platform teams have solved similar challenges. The path forward starts with understanding your current asset inventory gaps, and CloudQuery can help bridge them. Schedule a demo with our team today.
Written by

Try CloudQuery yourself
Self-hosted, open source, and free to start. Or schedule a demo to see the managed version.