As the Digital Operational Resilience Act (DORA) took effect on January 17, 2025, financial institutions with operations in the EU and their third party vendors must keep a close eye on their digital infrastructure. Compliance with DORA requires maintaining an accurate, real-time inventory of all cloud assets and regular checks to ensure everything meets strict security and compliance rules. This is where CloudQuery, a developer-first cloud governance platform, steps in, turning chaotic cloud data into actionable insights.
1. Understanding DORA
DORA sets out several key requirements:
- ICT Risk Management: Build a framework to identify, assess, and manage risks across all digital assets, including critical assets managed by third parties.
- Rigorous Incident Reporting: Quickly detect and report any IT incidents to reduce downtime.
- Regular Resilience Testing: Simulate disruptions to ensure systems can recover quickly.
- Manage Third-Party Risks: Hold vendors accountable for meeting security standards.
- Threat Intelligence Sharing: Partner with peers and regulators to stay ahead of threats.
Meeting these requirements is challenging without a centralized view of your cloud environment.
1. Why a Unified Asset Inventory Matters
DORA requires financial institutions to monitor their cloud environments continuously, keep detailed records of every digital asset and third-party service, and quickly identify and manage any vulnerabilities. A unified asset inventory is the foundation for meeting these goals. With CloudQuery, you can:
- Automated Asset Discovery: Connect AWS, Azure, GCP, or other providers to your Cloud Asset Inventory, and CloudQuery catalogs every VM, database, and storage bucket out of the box. No more spreadsheets, custom scripts or manual tracking.
- SQL-Powered Insights: CloudQuery transforms raw cloud data into a queryable database so you can write custom SQL queries to pinpoint issues relevant to DORA. Want to know which resources are misconfigured or have outdated security settings? A few SQL statements can provide those answers as will be shown in the upcoming sections.
- Benchmark Against Best Practices: CloudQuery offers pre-built security and compliance policies based on standards like CIS and NIST, so you can use these policies to quickly assess your environment without having to write every query from scratch.
These features and more enable you to identify misconfigurations, unencrypted resources, or unsecured endpoints—critical steps in maintaining operational resilience under DORA.
2. Building Your Cloud Asset Inventory
To get started, schedule a demo with our team to explore the CloudQuery platform. Once, you have access to the platform, you'll connect your cloud accounts—CloudQuery supports over 60 official integrations to bring together data from all your cloud and SaaS environments into one place.
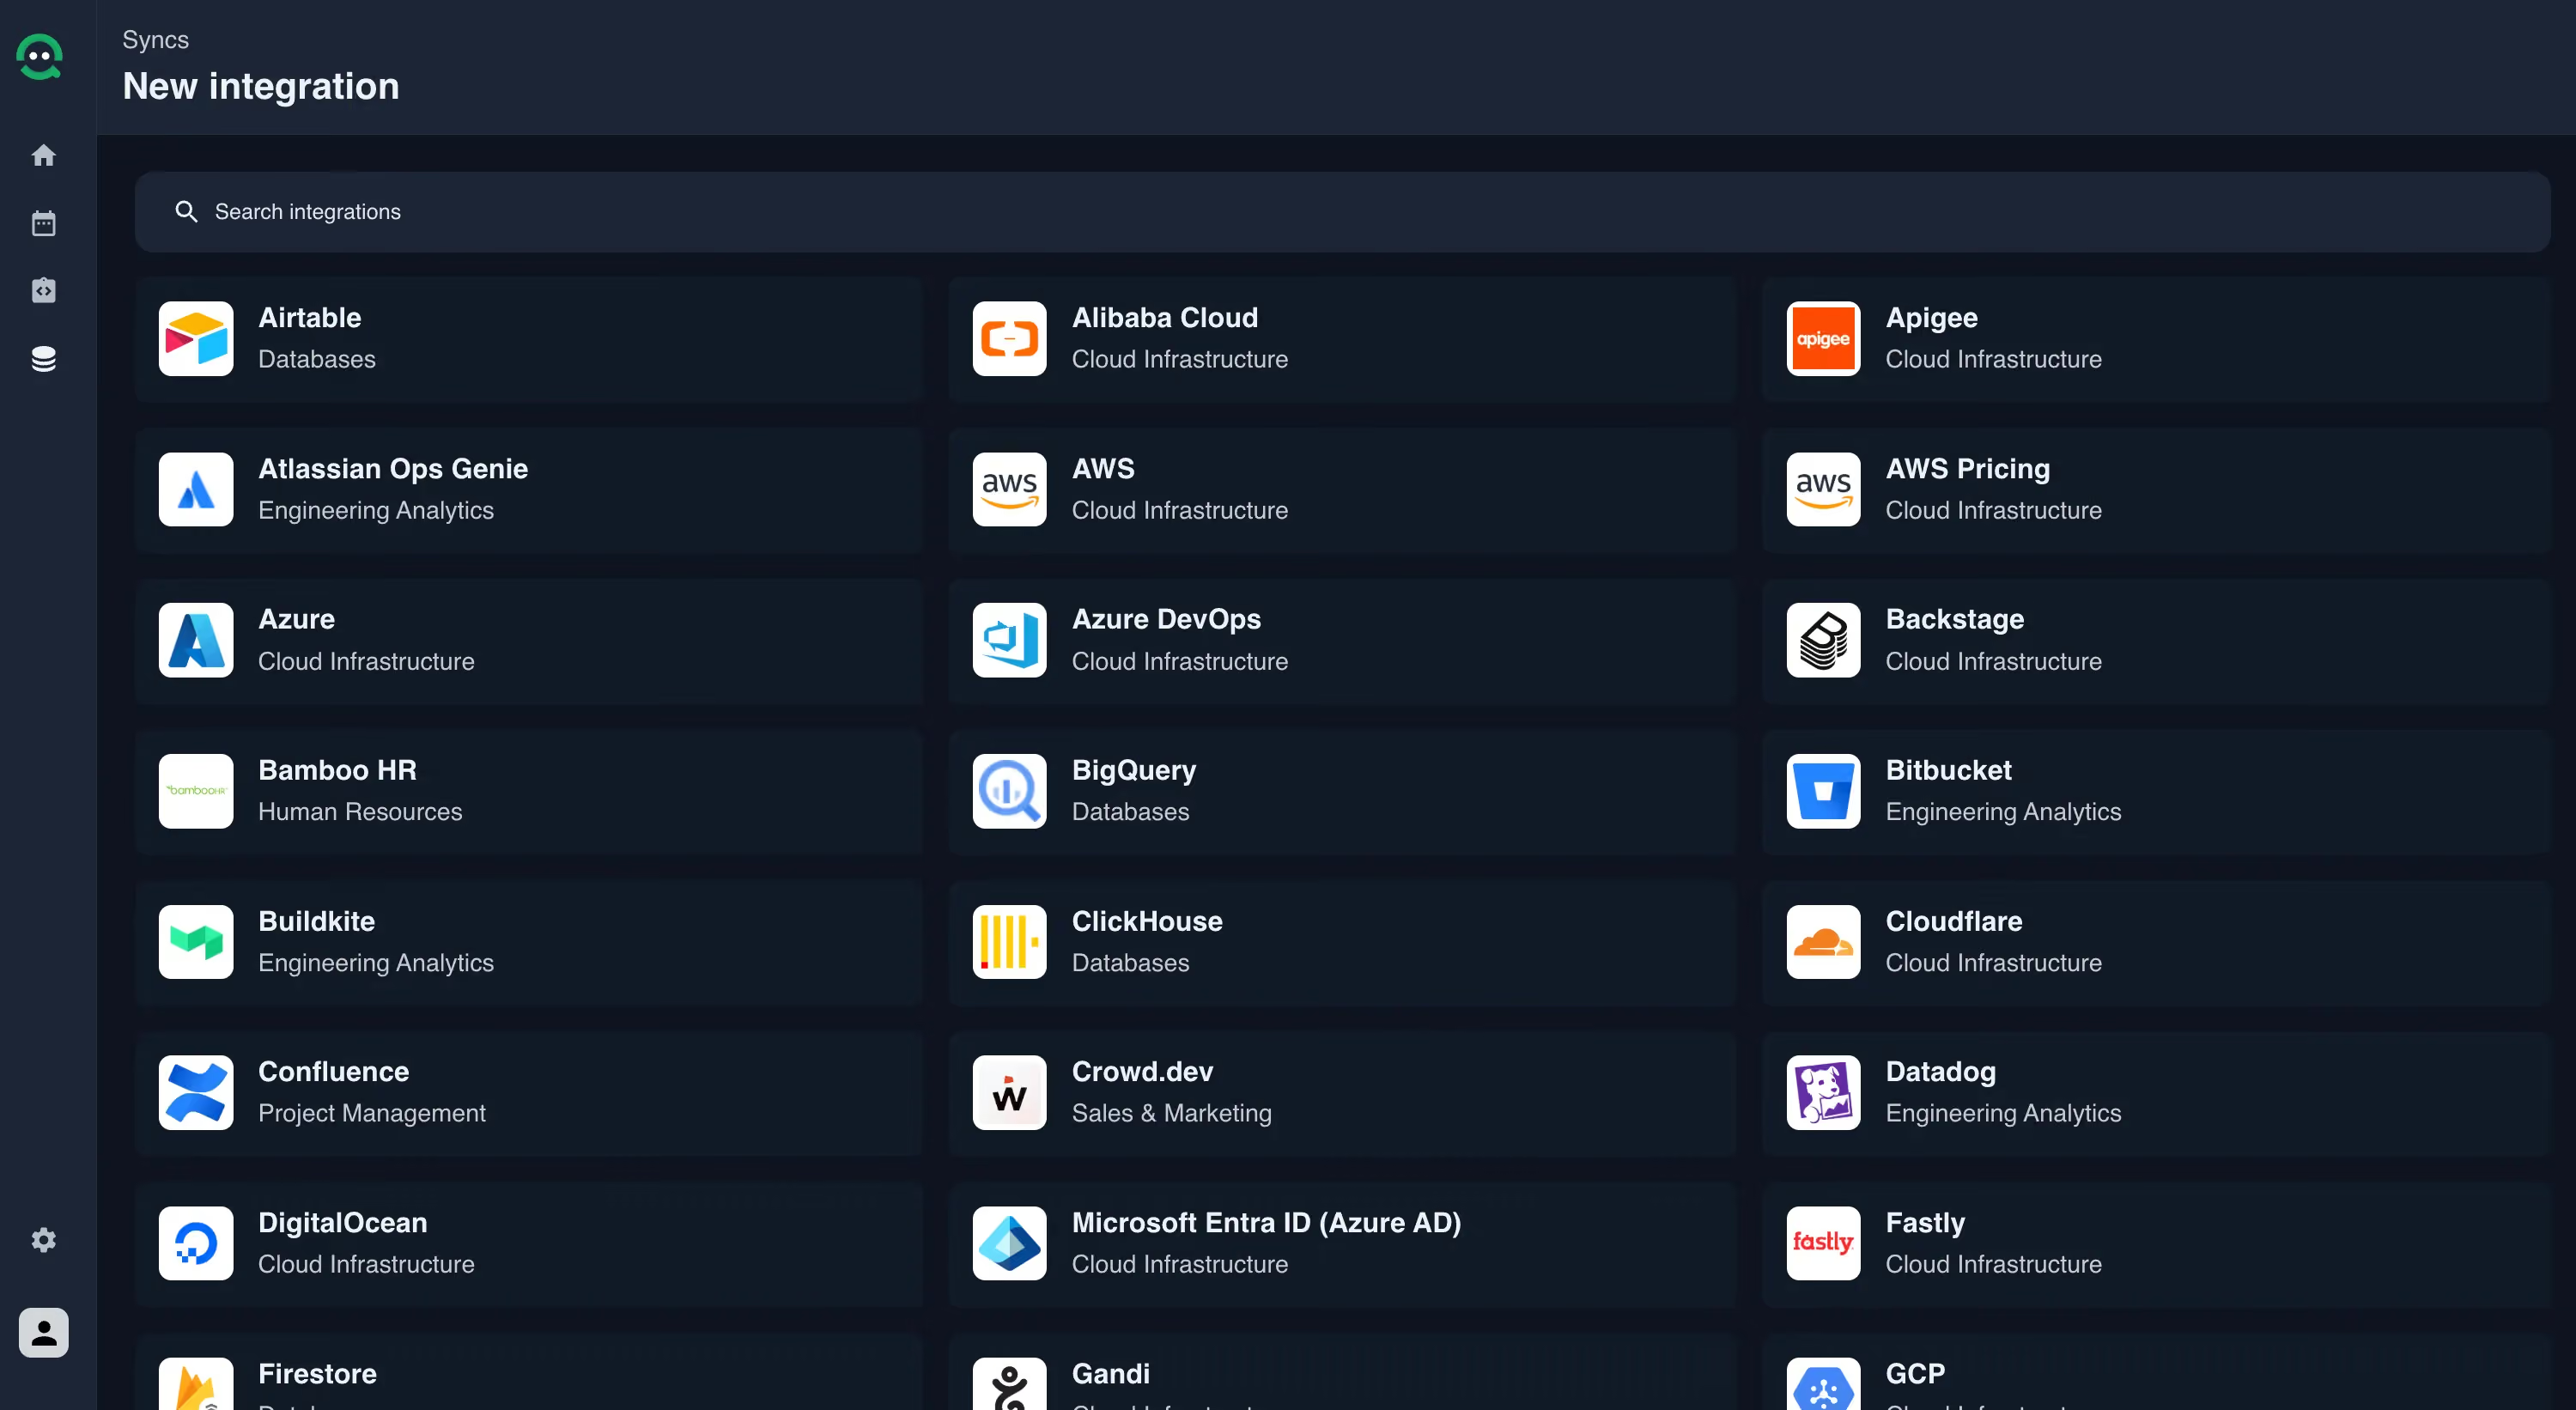
After connecting your accounts, CloudQuery automatically gathers asset data. You can then use pre-built filters to quickly check for untagged resources, filter by region or look at other metadata fields, giving you a high-level view of your cloud posture across multiple platforms.

3. Identify and Manage Risk with SQL Queries
Moreover, you can use the CloudQuery’s SQL console to dig deeper into your asset data. Below are some practical query examples to help you identify potential compliance gaps:
A. Identify Publicly Accessible Resources
Finding public resources helps you secure systems that are directly exposed to the internet, which is key for managing risks and reporting incidents under DORA.
This query lists EC2 instances that have a public IP address, which may require additional security controls:
B. Audit S3 Bucket Policies
Ensuring that storage buckets are secured against public access is critical for protecting sensitive financial data and meet DORA’s requirements.
This query finds S3 buckets that have overly open access policies, which might expose sensitive data:
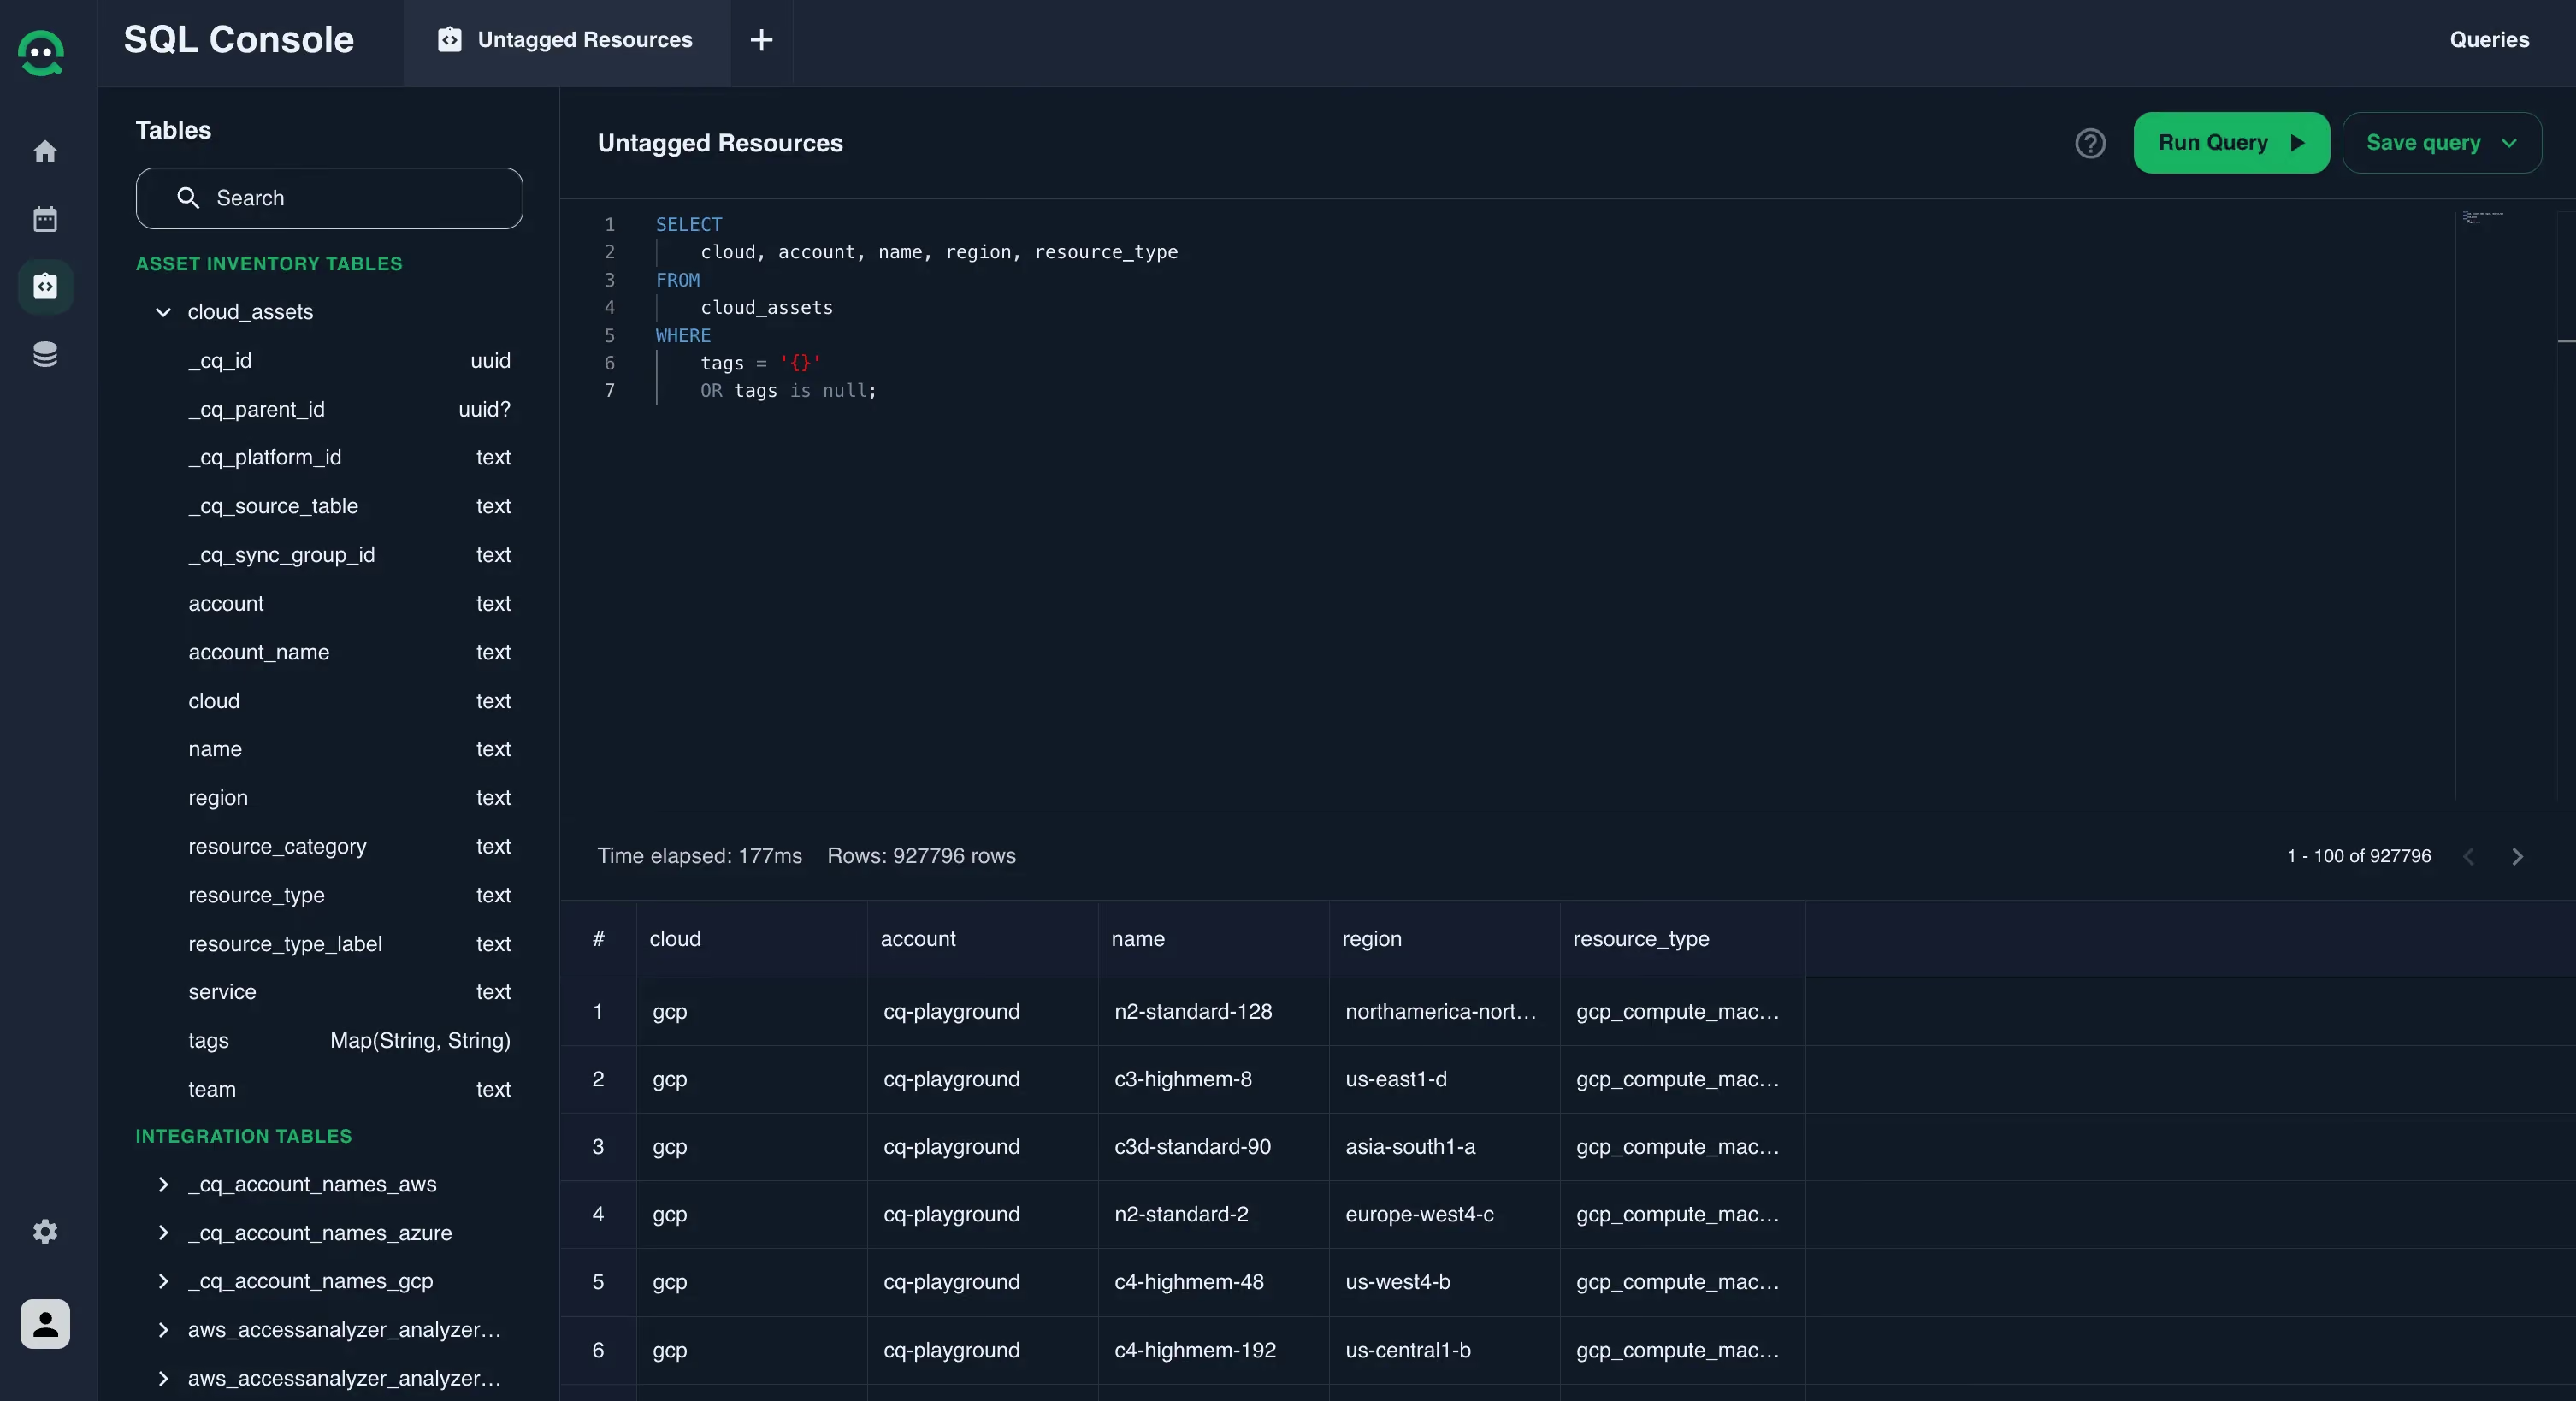
C. Identify Untagged Resources
Tags enable accountability. Untagged resources complicate incident response and audit trails.
This query helps you find resources that are missing tags, which are important for tracking assets and bringing accountability to cloud usage and spending.
D. Check RDS Backup Configurations
Automated backups are key for ensuring business continuity and rapid recovery after an incident.
This query finds AWS RDS instances that lack automated backup configurations:
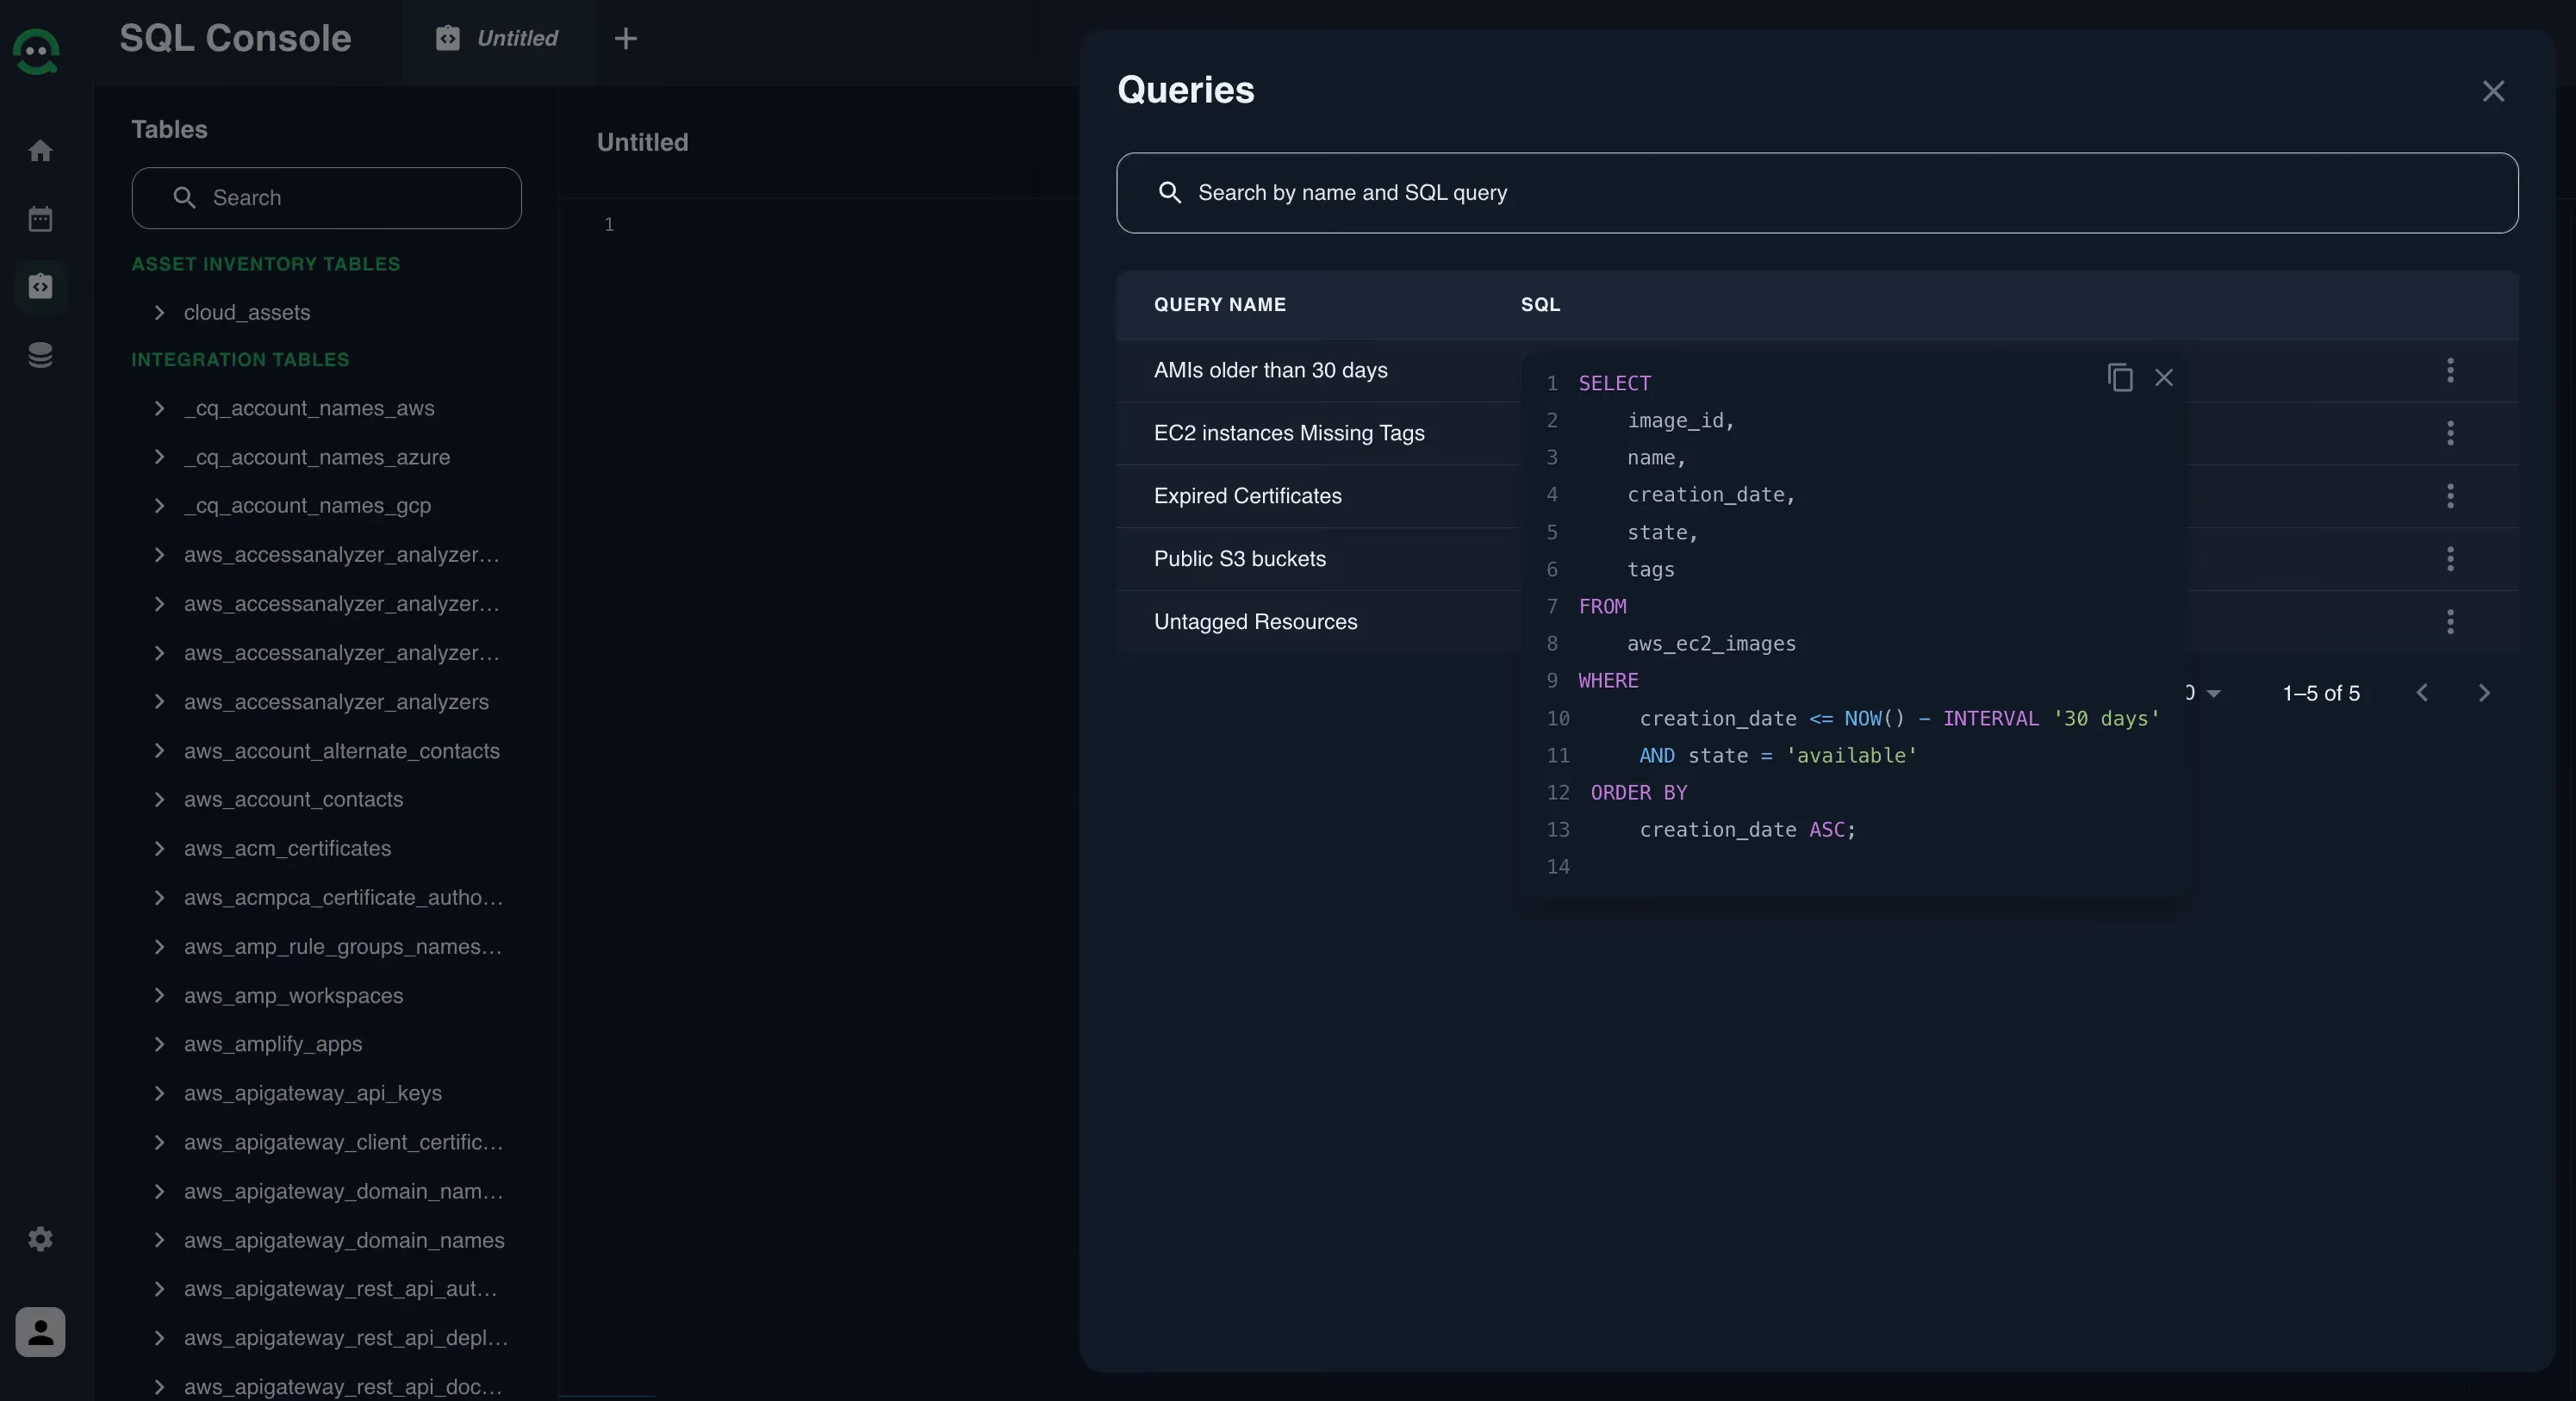
Save these queries to streamline compliance reporting and utilize our curated list of pre-built queries tailored to DORA requirements.
4. Leverage Security & Compliance Policies
Beyond custom queries, CloudQuery offers pre-configured security and compliance policies that automatically check your cloud environment against industry standards like CIS and NIST. For example, you can run a policy to ensure that IAM roles follow the principle of least privilege, reducing the risk of unauthorized access.
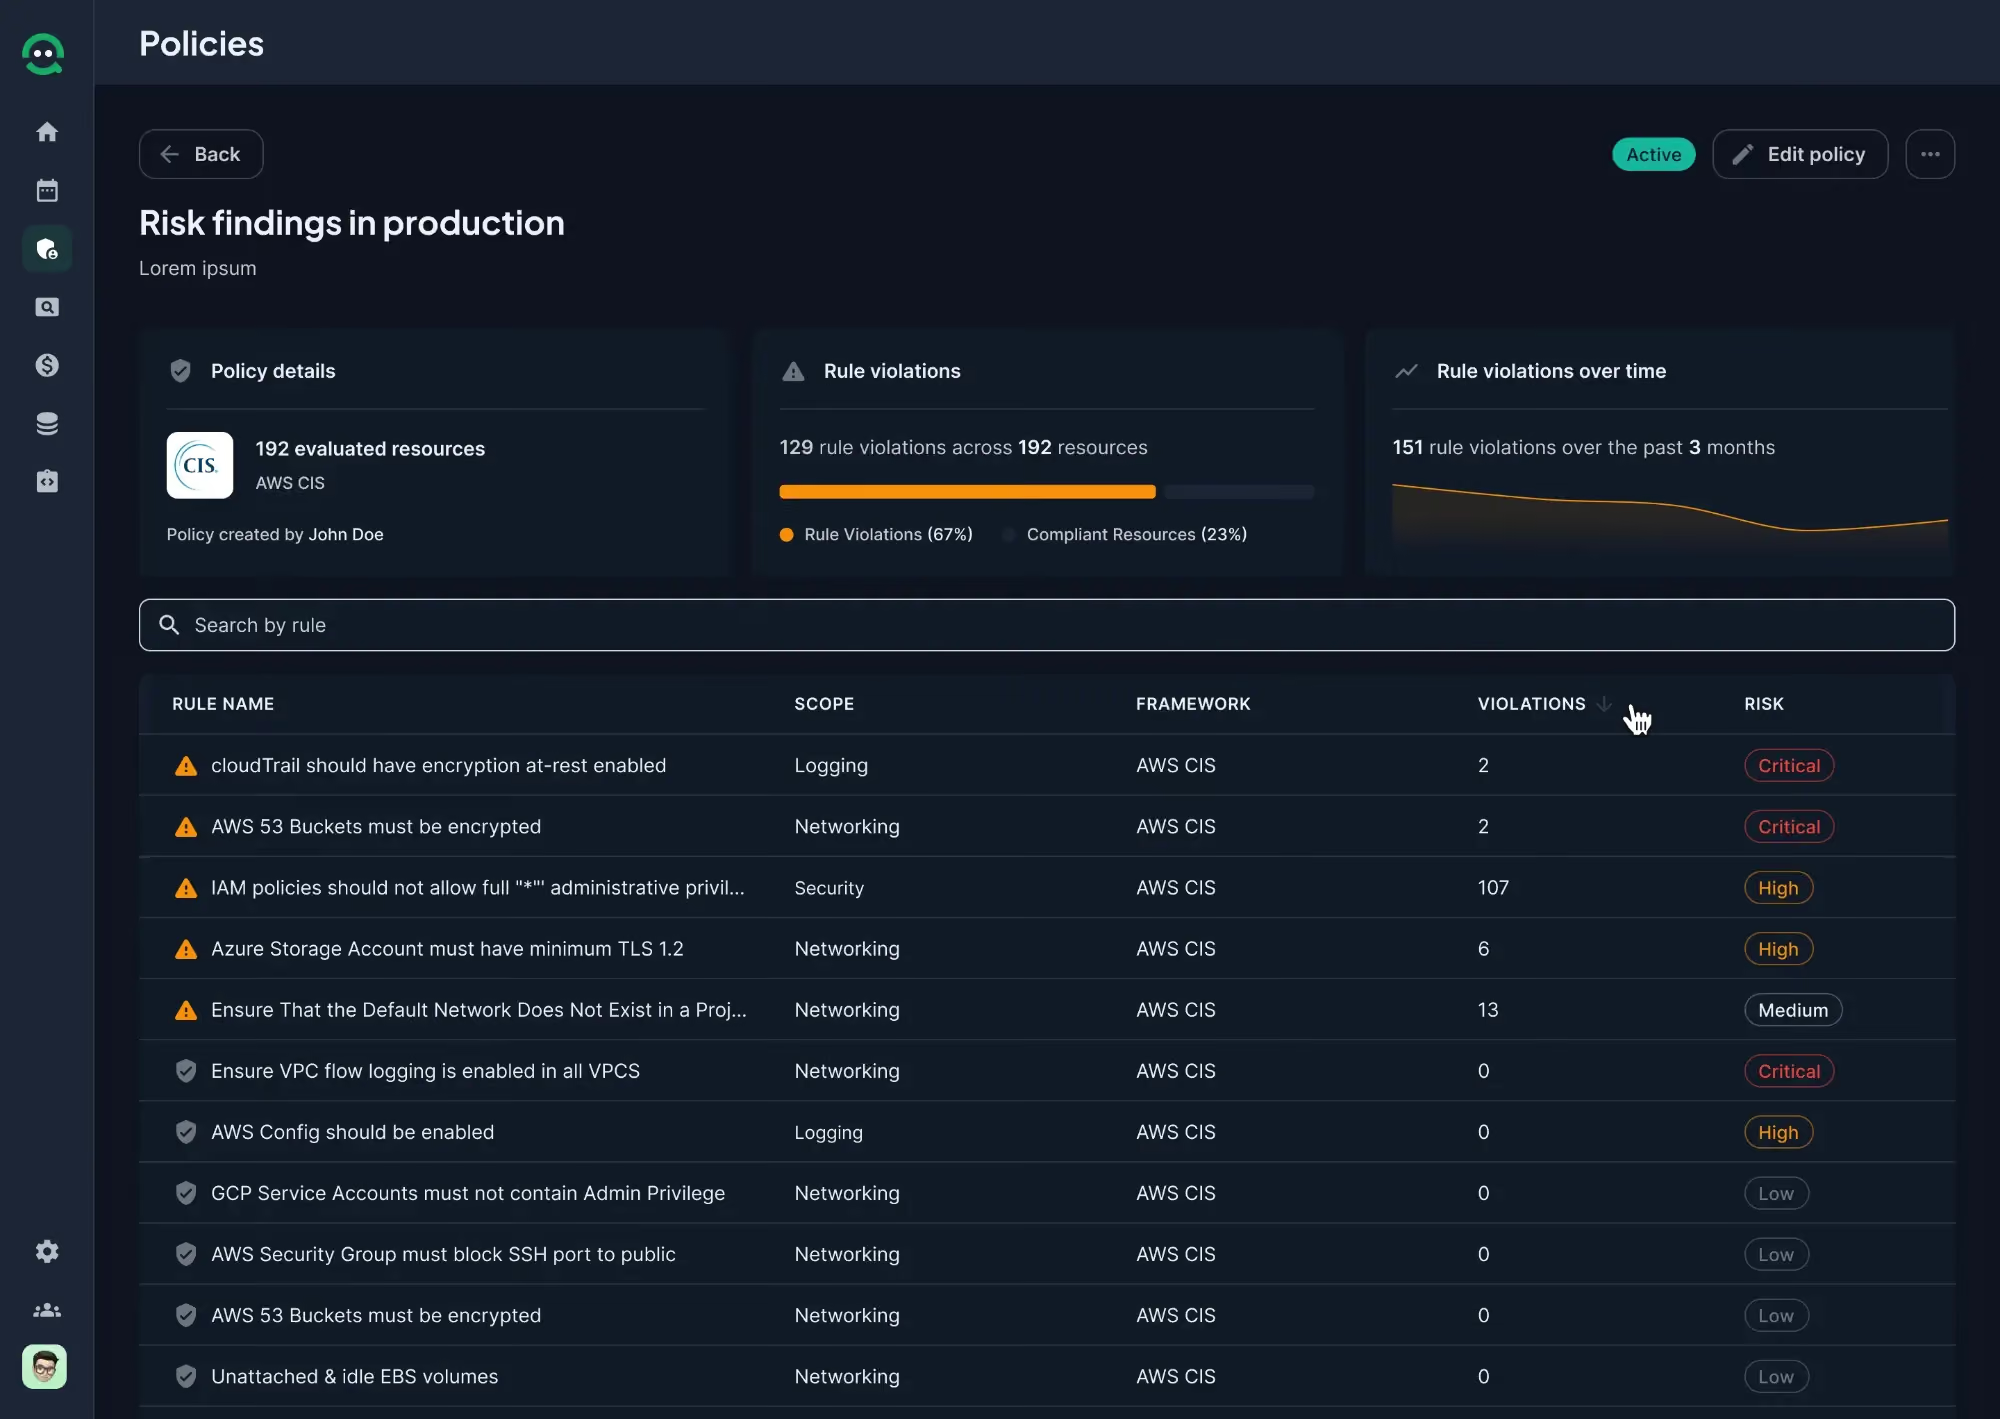
By integrating these policies into your workflow, you can make sure your cloud environment not only meet DORA’s strict standards but also follow best security practices overall.
Start using CloudQuery today to automate your asset inventory, evaluate your cloud configurations against compliance benchmarks, and ensure your institution is fully prepared for DORA. If you haven’t already, contact us to get started with CloudQuery today.
Have questions or need help? Join the CloudQuery Developer Community to connect with other users, share insights, and get support. Let us know how your team is tackling cloud security by engaging with us on LinkedIn, or X.
Written by
Try CloudQuery yourself
Self-hosted, open source, and free to start. Or schedule a demo to see the managed version.