AWS

Tutorials

How to Deploy CloudQuery into an AWS Organization

CloudQuery makes fetching resources from your entire organization simple, as long as you have the proper IAM trust relationships and permissions set up. In this blog post we will walk through one way of setting up these permissions so that you can have access to all of your configuration data in a single queryable database.

General Architecture

We will be deploying a single CloudFormation template in an admin account and then relying on CloudFormation StackSets to propagate the configurations to all of the member accounts. In the admin account we will create an IAM role that is able to list all of the accounts in the organization as well as assume a role in the member accounts. In the member accounts we will be deploying a single IAM role that has a trust policy to only allow the role in the admin account to assume it. The permissions for the IAM role in the member account are locked down so that the role can only access metadata about the configuration and never has access to your code or data.
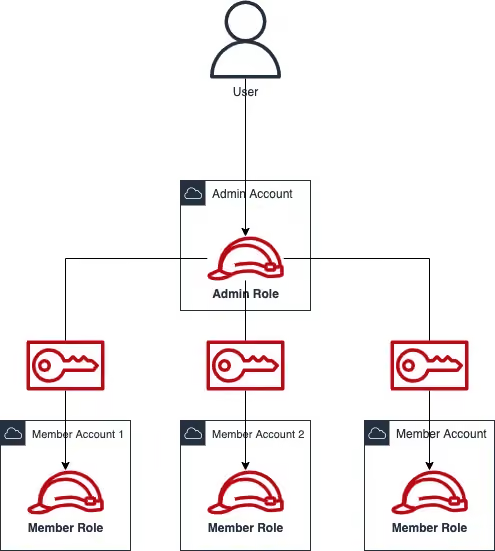
AWS Organization architecture diagram showing CloudQuery cross-account IAM role setup with StackSets

Prerequisites

  • CloudQuery binary installed and setup with a PostgreSQL database
  • AWS CLI V2 installed and configured
  • Admin access to the Root Account of your AWS Organization or an Account that is a Delegated Admin

Walk-through

Step 1: Clone Solution Repository

Clone the CloudQuery IAM-For-Orgs repository.

git clone https://github.com/cloudquery/iam-for-aws-orgs.git
cd iam-for-aws-orgs

Step 2: Deploy IAM Resources

Prior to using the AWS CLI to execute the following command but make sure to replace <ROOT_ORG_ID> with your Organizational Unit (OU) of the root (if you want to deploy to your entire organization). Or a comma separated list of OUs if you want to deploy it only to a specific set of accounts:

aws cloudformation create-stack \
--stack-name CloudQueryOrg-Deploy \
--template-body file://./template.yml \
--capabilities CAPABILITY_NAMED_IAM \
--parameters ParameterKey=OrganizationUnitList,ParameterValue=

You can monitor the state of CloudFormation deployment by running this command:

aws cloudformation describe-stacks \
--stack-name CloudQueryOrg-Deploy \
--query 'Stacks[].StackStatus | [0]'

Step 3: Ensure you can Assume role

Once the CloudFormation template has finished you will want to test out to make sure you can assume the role that was created in the Admin account. First you will get the ARN of that IAM role by running this command:

aws cloudformation describe-stacks \
--stack-name CloudQueryOrg-Deploy \
--query "Stacks[0].Outputs[?OutputKey=='AdminRoleArn'].OutputValue | [0]"

where the output should be a string like this:

"arn:aws:iam:::role/cloudquery-ro"

Once you have the ARN of the role that was created you can test out assuming it by running this CLI command:

aws sts assume-role \
--role-arn arn:aws:iam:::role/cloudquery-ro \
--role-session-name cloudquery-test

The output should look something like this:

{
"Credentials": {
"AccessKeyId": "ASIA...",
"SecretAccessKey": "...",
"SessionToken": "...",
"Expiration": "2022-07-12T17:38:11+00:00"
},
"AssumedRoleUser": {
"AssumedRoleId": "...",
"Arn": "arn:aws:sts:::assumed-role/cloudquery-ro/cloudquery-test"
}
}

Step 4: Update your CloudQuery Configuration File

Now that you have properly configured the IAM role in the Admin account you can take the 2 outputs from the CloudFormation stack and plug them into your CloudQuery configuration file

aws cloudformation describe-stacks \
--stack-name CloudQueryOrg-Deploy \
--query "Stacks[].Outputs"

Where the output should be in this form:

[
[
{
"OutputKey": "MemberRoleName",
"OutputValue": "cloudquery-ro"
},
{
"OutputKey": "AdminRoleArn",
"OutputValue": "arn:aws:iam:::role/cloudquery-ro"
}
]
]

Here is an example configuration that makes use of the resources you just created

kind: source
spec:
name: aws-0
path: cloudquery/aws
registry: cloudquery
version: 'v34.9.0'
tables: ['*']
destinations: ['postgresql']
spec:
aws_debug: false
org:
admin_account:
role_arn:
member_role_name:
regions:
- '*'

Step 5: Run Sync

Now you are all set to be able to execute a fetch and grab resources from your whole AWS Organization

cloudquery sync

Summary

In this walk-through we deployed a CloudFormation template that created the appropriate AWS IAM roles that CloudQuery needs in order to fetch resources from all accounts in an AWS Organization. Then you used the outputs from that template to configure CloudQuery to fetch resources from the member account.

After you have this working on your local machine you can check out our Terraform module for simplifying the deployment of CloudQuery into a production ready environment!

Want to see CloudQuery in action? Schedule a demo with our team or check out the platform documentation to learn more.

Want help getting started? Join the CloudQuery community to connect with other users and experts, or message our team directly here if you have any questions.

Try CloudQuery yourself

Self-hosted, open source, and free to start. Or schedule a demo to see the managed version.
Related posts

AWS

Security

Tutorials

Finding AWS Unrestricted Outbound Access in 2026: EC2, Lambda, and Beyond

Find EC2, Lambda, and ECS Fargate resources with unrestricted outbound access in AWS using SQL. Why egress controls still break attack chains in 2026.

Joe Karlsson

Joe Karlsson

May 5, 2026

AWS

Security

Tutorials

AWS IAM Identity Center with Google Workspace as an IdP: 2026 Step-by-Step Guide

Set up AWS IAM Identity Center with Google Workspace: SAML authentication, SCIM user provisioning, and group sync with CLI or ssosync. Updated for 2026.

Joe Karlsson

Joe Karlsson

May 5, 2026

AWS

Cloud Infrastructure

Security

Tutorials

Integrate AbuseIPDB Threat Intelligence with CloudQuery

Enrich your cloud asset inventory with AbuseIPDB threat intelligence to identify public cloud IPs with known abuse reports.

Joe Karlsson

Joe Karlsson

April 20, 2026

AWS

Cloud Infrastructure

Tutorials

How to Query ipinfo.io Data with CloudQuery

Learn how to enrich your cloud asset inventory with ipinfo.io IP geolocation and threat intelligence data using CloudQuery.

Joe Karlsson

Joe Karlsson

April 20, 2026

AWS

Security

Tutorials

AWS IAM Identity Center (Formerly AWS SSO): The Complete 2026 Guide

AWS IAM Identity Center replaced AWS SSO in 2022. Learn how to set it up, configure permission sets, use the AWS CLI, and audit access with CloudQuery.

Joe Karlsson

Joe Karlsson

April 6, 2026

AWS

Tutorials

AWS Pinpoint Is Being Deprecated: How to Assess Your Migration Scope

AWS Pinpoint reaches end of support October 2026. Query your Pinpoint usage across all accounts to find what needs migrating before the deadline.

Joe Karlsson

Joe Karlsson

March 24, 2026

AWS

Best Practices

Tutorials

CloudQuery Sync Performance: A Practical Troubleshooting Guide

Diagnose why CloudQuery syncs slow down after plugin upgrades, identify expensive tables, and use the CLI command that replaces the tables wildcard.

Joe Karlsson

Joe Karlsson

March 6, 2026

AWS

Security

Tutorials

Set Up AWS CLI with SSO (IAM Identity Center) — Step by Step

Configure AWS CLI v2 with IAM Identity Center in 5 minutes. Covers sso-session setup, automatic token refresh, and switching between multi-account profiles.

Yevgeny Pats

Yevgeny Pats

February 25, 2026

AWS

Cloud Infrastructure

Tutorials

AWS Lambda Python 3.9 End-of-Support: Find and Upgrade Every Affected Function

AWS Lambda Python 3.9 security patches stopped Dec 15, 2025. Find every affected function across all accounts with SQL queries and upgrade to 3.12 or 3.13.

Joe Karlsson

Joe Karlsson

February 10, 2026

Own your pipeline.
Own your data.