AWS

Security

Tutorials

How to Set Up Cross Account Access in AWS with AssumeRole

In this how-to guide we will walk through how to create a role in an external account that we want to AssumeRole into. In our example we will provide the new role in the external account with broad ReadOnly permissions (but you are free to change to whatever you want).

AWS cross-account access architecture diagram showing AssumeRole flow between Account A and Account B

Introduction to AWS IAM

If you are familiar AWS IAM feel free to skip this section. But here is a quick recap: AWS IAM is the underlying service that AWS services rely on for authorization. While there are many ways of getting valid AWS credentials (setting up AWS SSO) this blog is going to focus on how you can use those credentials once you have them. Before we dive in a few high level concepts that we need to clarify:

  • Credentials used to sign API calls are always associated with a single user or role entity.
  • A user is a single identity that is able to use long lived credentials while a role is a short lived identity that can be temporarily assumed by other entities.
  • Credentials are authorized to perform only the actions that are defined in the policies that are associated with the role or user, and the scope of those permissions can never grant access to a resource in another account.

This means that a single policy cannot grant User in Account A access to a resource in Account B. A common scenario is for one user or role to access resources in Account B for use cases such as auditing and monitoring. In order for a user in Account A to access a resource in a different Account they must get access to credentials that are from Account B. The most common and secure way to enable User A in Account A to access resource B in Account B is done via cross account role assumption. This means that Account B defines a role, Role-B, that has a Trust Policy that says that entities from Account A are allowed to assume it, this effectively means that entities from Account A are able to get credentials that have the access of Role-B. So once that is in place User-A is able to assume Role-B and use the new credentials to interact with Resource-B.

Walkthrough

In this tutorial we will show you how to do in the console (ClickOps) but feel free to automate it via your favorite IaC.

Step 1

Go to iam→roles and click Create Role

AWS IAM console Create Role page showing trusted entity type selection options

Step 2

For Trusted Entity, Choose AWS account, click Another AWS account and fill-in the account id you want to access from and click next

AWS IAM trusted entity configuration screen for cross-account access with Another AWS account option

Step 3

Attach the Permission policy you want this role to have. In our case we will attach ReadOnlyAccess - mark the checkbox and click next.
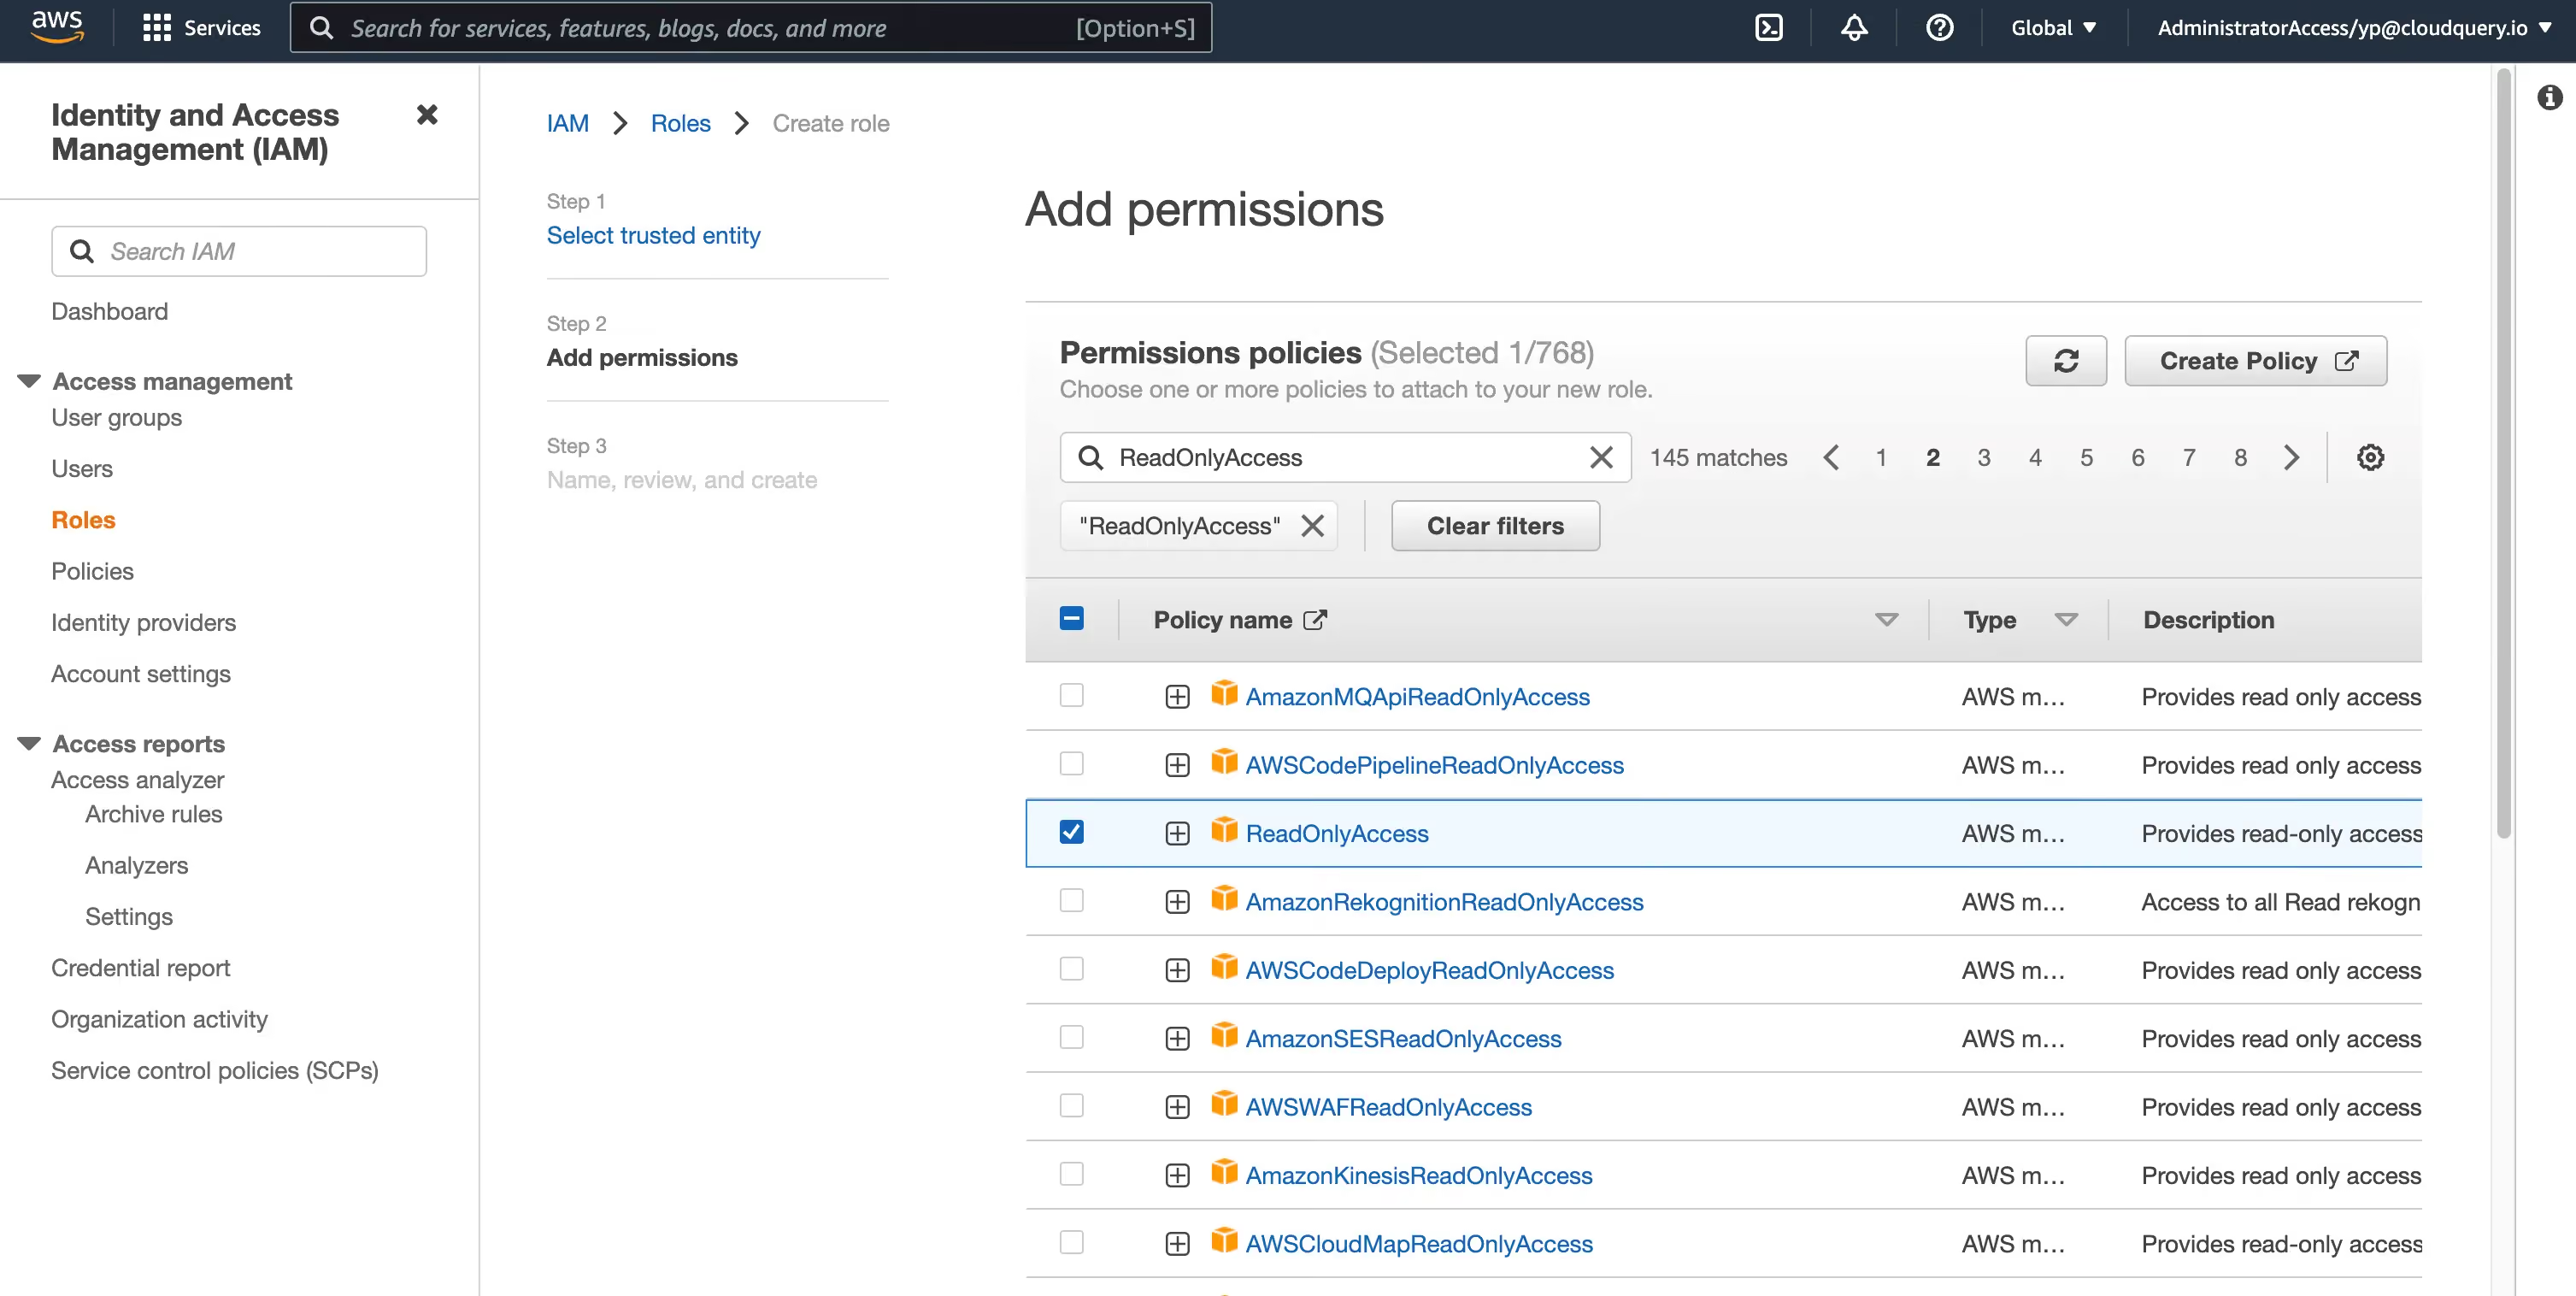
AWS IAM Add permissions page showing ReadOnlyAccess policy selection for cross-account role

Step 4

Last screen should look like the following and you should name the role the same name in all accounts you want to AssumeRole into. In this case we marked it as CrossAccountReadOnlyRole

AWS IAM Review role screen displaying CrossAccountReadOnlyRole configuration with trust policy details

Step 5

Repeat 1-4 for each account you want to access from.

Step 6

Login into your account where you want to assume role from and go to IAM→policies and click Create Policy. Paste the following policy in the JSON tab

{
"Version": "2012-10-17",
"Statement": [
{
"Sid": "VisualEditor0",
"Effect": "Allow",
"Action": "sts:AssumeRole",
"Resource": "arn:aws:iam::*:role/CrossAccountReadOnlyRole"
}
]
}

So it should look something like the following:

AWS IAM Create policy JSON editor showing AssumeRole permissions for cross-account access

Step 7

Click Next, give it tags and then pick a name. We will use CloudQueryCrossAccountReadOnlyAccess

AWS IAM Review policy screen for CloudQueryCrossAccountReadOnlyAccess with policy summary

Step 8

Now you can go to user or role that you use in your main account and attach the policy:

AWS IAM attach policy screen showing CloudQueryCrossAccountReadOnlyAccess being added to user or role

Step 9

That’s it! You are done now you can use assume role via this role.

Want to see CloudQuery in action? Schedule a demo with our team or check out the platform documentation to learn more.

Want help getting started? Join the CloudQuery community to connect with other users and experts, or message our team directly here if you have any questions.

Try CloudQuery yourself

Self-hosted, open source, and free to start. Or schedule a demo to see the managed version.
Related posts

AWS

Security

Tutorials

Finding AWS Unrestricted Outbound Access in 2026: EC2, Lambda, and Beyond

Find EC2, Lambda, and ECS Fargate resources with unrestricted outbound access in AWS using SQL. Why egress controls still break attack chains in 2026.

Joe Karlsson

Joe Karlsson

May 5, 2026

AWS

Security

Tutorials

AWS IAM Identity Center with Google Workspace as an IdP: 2026 Step-by-Step Guide

Set up AWS IAM Identity Center with Google Workspace: SAML authentication, SCIM user provisioning, and group sync with CLI or ssosync. Updated for 2026.

Joe Karlsson

Joe Karlsson

May 5, 2026

AWS

Cloud Infrastructure

Security

Tutorials

Integrate AbuseIPDB Threat Intelligence with CloudQuery

Enrich your cloud asset inventory with AbuseIPDB threat intelligence to identify public cloud IPs with known abuse reports.

Joe Karlsson

Joe Karlsson

April 20, 2026

AWS

Security

Tutorials

AWS IAM Identity Center (Formerly AWS SSO): The Complete 2026 Guide

AWS IAM Identity Center replaced AWS SSO in 2022. Learn how to set it up, configure permission sets, use the AWS CLI, and audit access with CloudQuery.

Joe Karlsson

Joe Karlsson

April 6, 2026

AWS

Security

Tutorials

Set Up AWS CLI with SSO (IAM Identity Center) — Step by Step

Configure AWS CLI v2 with IAM Identity Center in 5 minutes. Covers sso-session setup, automatic token refresh, and switching between multi-account profiles.

Yevgeny Pats

Yevgeny Pats

February 25, 2026

AWS

GCP

Security

Tutorials

How to Inventory All Public IP Addresses Across AWS and GCP using CloudQuery

Track every public IP across AWS and GCP in minutes with SQL. Find exposed EC2 instances, unused Elastic IPs, and GCP Compute resources in one place.

Adam Cobb

Adam Cobb

Joe Karlsson

Joe Karlsson

December 19, 2025

AWS

Azure

GCP

Security

Tutorials

How to Find Internet-Facing Cloud Assets in AWS, Azure and GCP

Find all internet-facing cloud resources across AWS, Azure, and GCP. Identify exposed VMs, storage, databases, and load balancers to reduce attack surface.

Adam Cobb

Adam Cobb

November 5, 2025

AWS

Security

Tutorials

DORA Compliance Made Simple with CloudQuery

Ensure DORA compliance with CloudQuery. Automate cloud asset inventory, run SQL-powered audits, and benchmark against security best practices.

Mohamed Labouardy

Mohamed Labouardy

February 10, 2025

AWS

Security

Tutorials

How To List All Expired SSL Certificates on AWS

Learn how to identify expired AWS SSL/TLS certificates using CloudQuery. Sync your AWS data, run SQL queries, and consolidate results to ensure cloud security.

Joe Karlsson

Joe Karlsson

February 5, 2025

Own your pipeline.
Own your data.