The True Cost of Poor Tagging in Cloud Environments (and How to Fix it)
Ah, tagging. The thing every cloud architect swears they’ll enforce religiously, only for it to turn into a chaotic mess three sprints later. It starts with good intentions: “Let’s just tag everything properly so we can track costs.” Then reality slaps you in the face. Someone forgets. Someone leaves. Someone creates 500 instances named test-server-123 and then vanishes like a ghost.
And what does that leave you with? A bill big enough to make your CFO break out in hives.
The moral is that you can’t control what you don’t see, and you can’t see what you don’t tag.
Tagging might seem like a minor detail in cloud management, but in reality, it’s one of the most important parts of cloud governance. Without proper tagging, companies struggle to track cloud resources, leading to wasted spend, security risks, and compliance issues.
In this blog, we’ll explore the actual cost of poor tagging and how CloudQuery provides a unified solution to bring clarity to your cloud infrastructure.
The true cost of poor tagging
Tagging is a critical element in cloud governance because it provides essential context around every cloud resource. Without this context, managing cloud infrastructure becomes challenging, making cost optimization, security, and compliance efforts significantly more difficult and time consuming. Poor tagging practices can directly lead to higher operational costs, security breaches, and regulatory issues.
Specifically, inadequate tagging can impact your organization in several significant ways:
1. Wasted cloud spend
Organizations frequently waste considerable financial resources due to inadequate tagging. According to Flexera's 2024 State of the Cloud Report, approximately 32% of cloud spend is wasted on underutilized or orphaned resources that lack proper tagging. Without clearly defined tags, cloud teams cannot effectively identify ownership or track usage, leading to unnecessary expenses that continue unnoticed.
For example, a company running multiple projects simultaneously might leave cloud instances active even after projects conclude. Without proper tags, identifying and terminating these resources becomes tricky, resulting in significant avoidable costs accumulating over time.
2. Security risks and data breaches
Organizations frequently face significant security vulnerabilities due to improper tagging. Gartner's research highlights that poorly managed cloud environments, especially those without resource tagging, often lead to unnoticed security gaps. Without proper tagging, security teams struggle to quickly identify and mitigate risks, allowing vulnerabilities to persist and potentially leading to damaging data breaches.
For instance, an enterprise SaaS provider inadvertently left a storage bucket containing customer data publicly accessible. Because this bucket was untagged and, therefore, unmonitored, the security team overlooked it, resulting in a major data breach.
3. Compliance nightmares
Regulated industries face severe compliance risks when tagging is inadequate. According to industry analyses, unclear and inconsistent tagging complicates regulatory compliance audits significantly, increasing the risk of penalties and legal consequences. Without effective tagging practices, organizations cannot reliably demonstrate adherence to required standards.
For example, a healthcare organization encountered substantial challenges during a HIPAA compliance audit due to inconsistent tagging. The inability to clearly identify and verify resource management practices led to audit failures and compliance penalties.
Why better tagging saves you money
CloudQuery provides a powerful, real-time SQL-based platform designed specifically to address cloud tagging issues by simplifying cloud governance and significantly improving visibility across your cloud environment.
CloudQuery makes it easy to build a comprehensive cloud asset inventory by automatically pulling resources from all your cloud providers into one unified data store. With hundreds of plugins, you can add even more resources to your cloud asset inventory.
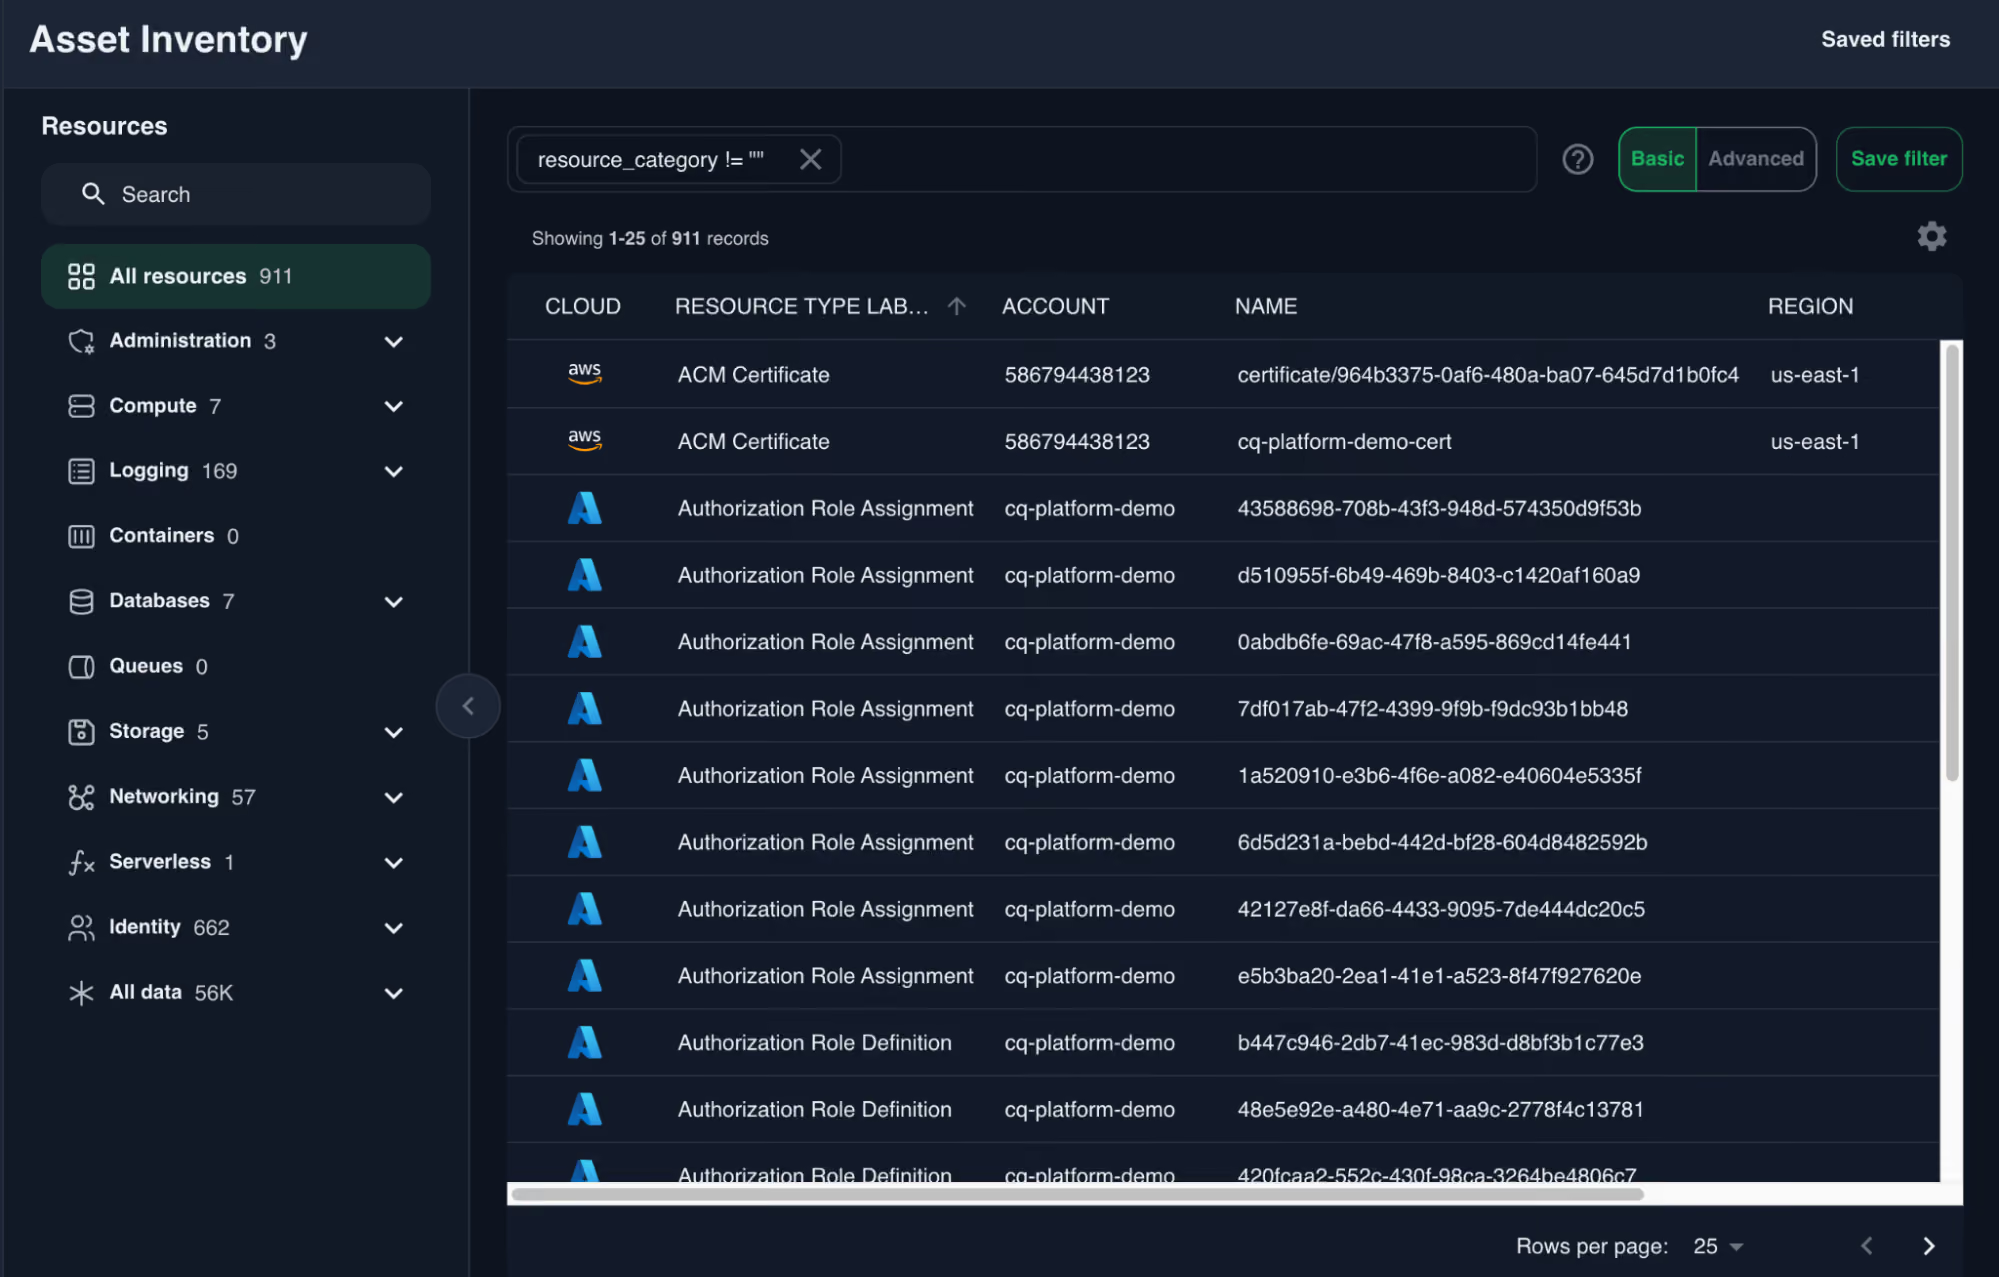
Using familiar SQL queries, your teams can instantly search, analyze, and gain valuable insights about your infrastructure, enabling rapid identification of resources that require attention. You can even save them for future use.

Ok, great! We now know how powerful CloudQuery can be. But how can we put this into practice to ensure tags are back under control?
Show Me the (Saved) Money
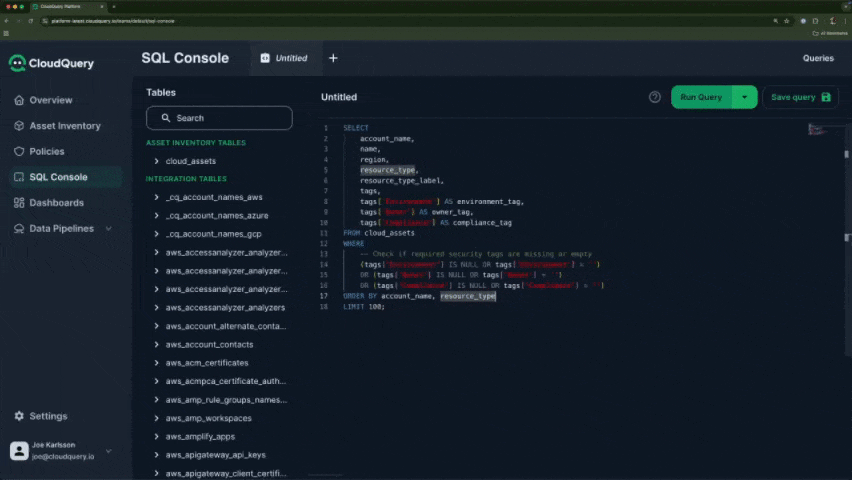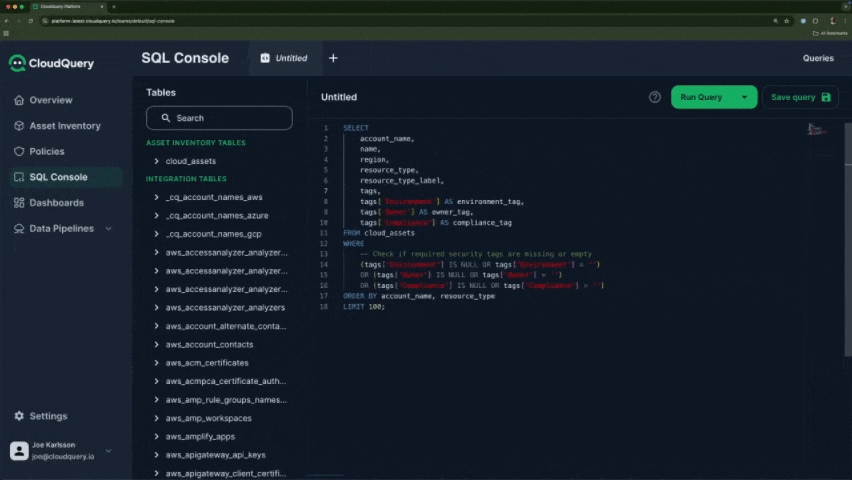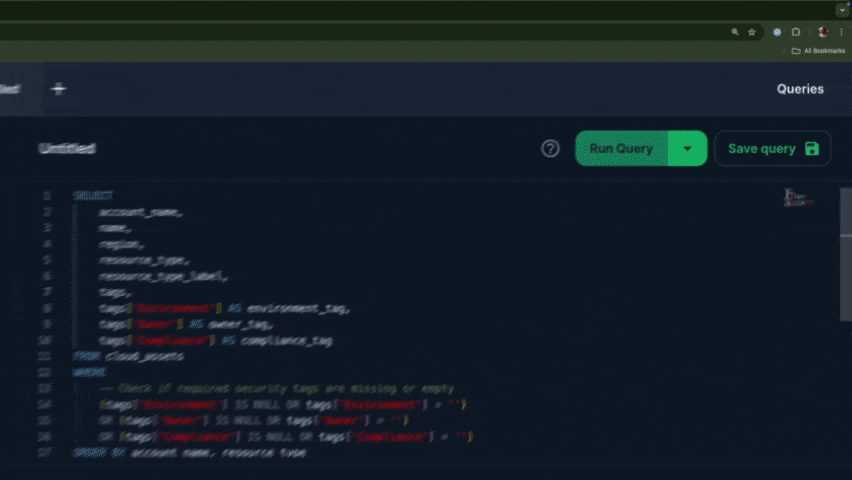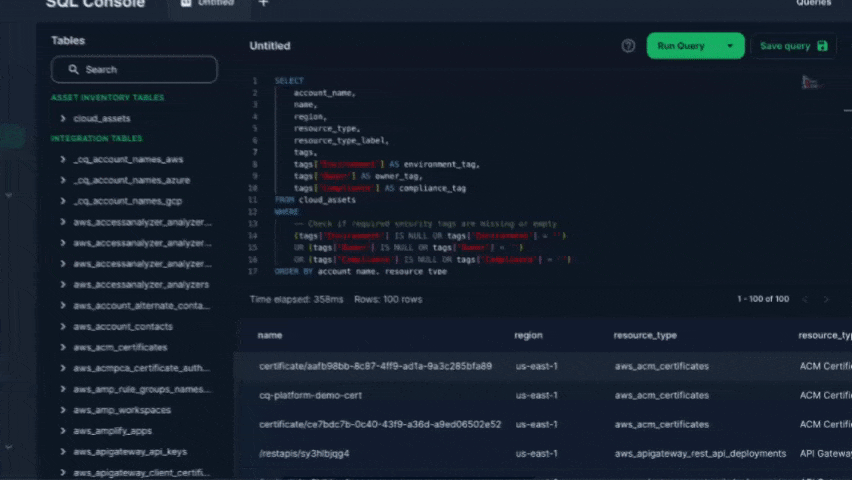
Let’s be real. Every engineer knows they should enforce tagging, but no one has time to check every instance manually. With CloudQuery, teams can instantly find and address tagging gaps, enabling quick identification of orphaned, untagged, or idle resources. With one simple query, you can find them all:
How to Detect Untagged Cloud Resources
Boom. Instant clarity.
Now, instead of hoping people tag things correctly, you can find the gaps, fix them, and stop paying for stuff you don’t use. This isn’t just cleaning up, this is cost-cutting without making anyone cry.
Strengthen cloud security
Security in the cloud is like flossing, everyone knows they should do it, but a shocking number of people don’t. And then one day, boom, breach, compliance violation, or an auditor with a look that says, “This is going to hurt.”
Tagging isn’t just about saving money. It’s one of the easiest ways to track security and compliance. If your resources aren’t properly tagged, you have no clue who owns them, what environment they belong to, or whether they’re even following security policies. That’s how shadow IT, unauthorized access, and compliance violations happen.
This query can help detect misconfigured or non-compliant security tags by checking if required security-related tags (e.g., Environment, Owner, Compliance) are missing or incorrectly set.
How to Audit Cloud Security Tags for Compliance and Security
Missing security tags can turn your cloud into a compliance nightmare, leaving critical gaps that auditors, hackers, and regulators love to exploit. Without proper tagging, resources become untraceable, making ownership disputes and security risks inevitable, especially when public-facing assets are involved. This query acts as your early warning system, identifying missing environment, owner, and compliance tags before they lead to costly fines or breaches. It also makes audits painless by keeping everything properly labeled and policy violations in check, so you stay ahead of security issues instead of cleaning up after them.
Final thoughts and next steps
Effective tagging isn't simply about staying organized, it's essential for maintaining control, ensuring security, optimizing costs, and complying with your governance policies within your cloud infrastructure. Without a robust tagging strategy, you risk hidden costs, security vulnerabilities, and compliance headaches.
CloudQuery provides a unified, real-time visibility platform that brings clarity and control back into your cloud environment. Through automated tagging audits, intuitive SQL queries, and customizable governance frameworks, CloudQuery empowers your teams to proactively manage and secure your cloud resources. For teams dealing with tagging gaps at scale, CloudQuery Insights surfaces those gaps automatically alongside cost and security findings, so the full picture for each resource is already there when you need it.

Don't let poor tagging undermine your cloud strategy, gain full visibility and governance with CloudQuery.
Request a demo today to see how much you could save.
Written by

Try CloudQuery yourself
Self-hosted, open source, and free to start. Or schedule a demo to see the managed version.